
Autonomous AI penetration testing is here and your current defenses were not built for it
ARTEX and tools like it put multi-agent LLM attack systems in adversaries' hands. Here is what that means for your security posture in 2026.
ARTEX — a multi-agent LLM penetration testing framework written in Go and Next.js — won Baidu's Agent+ Offensive and Defensive Challenge on September 3, 2026, and accumulated over 1,200 GitHub stars in its first week of public availability. It is not a research curiosity. It is a working autonomous system that plans, executes, and adapts attack chains without a human at the keyboard between steps. The project's own developers converted it to closed source on October 8, 2026, after attackers weaponized the open-source edition and caused several large-scale security incidents in the financial services industry — the clearest possible confirmation that this threat class is already live, not hypothetical.
That distinction matters more than most security teams have processed yet.
Traditional penetration testing is linear. A human tester identifies a vector, attempts exploitation, documents the result, pivots. The feedback loop is measured in hours or days. ARTEX-class systems compress that loop to seconds. The agent selects tools, interprets outputs, updates its attack graph, and continues — across multiple parallel sub-agents coordinating over the Model Context Protocol. OWASP's LLM Top 10 (2025 revision) lists Excessive Agency and Insecure Plugin Design as the first and third most critical risks for exactly this reason: when agents can act without human confirmation and chain tool calls autonomously, the blast radius of a compromised or weaponized agent expands dramatically.
The threat model has changed at the infrastructure layer
Consider what autonomous offensive agents do differently from the attack patterns most managed security programs were designed to detect.
- Reconnaissance is continuous, not episodic. An agentic attacker does not schedule a scan. It observes, waits, and re-probes based on environmental signals. Signature-based detection built around scan bursts will miss it.
- Attack paths are generated, not enumerated. Human testers work from a known playbook. LLM-driven agents generate novel chains by reasoning over target topology. The MAST taxonomy's Lateral Movement and Privilege Escalation categories both expand when the attacker can reason about the environment rather than pattern-match against a checklist.
- Dwell time shrinks while sophistication grows. The 2025 Mandiant M-Trends report put global median dwell time at 11 days, down from 16 in 2023. Agentic attackers do not need dwell time to plan — planning happens in milliseconds — so the detection window before meaningful damage narrows further.
NIST AI RMF Govern 1.2 requires organizations to identify and document the technical threats specific to AI systems in their environment. That obligation now runs in both directions: you must assess the AI systems you deploy, and you must assess the AI-augmented threats targeting your non-AI infrastructure.
Why MCP is the attack surface no one is patching
ARTEX coordinates its sub-agents over MCP. That is not incidental. MCP has become the de facto wiring layer for agentic AI in enterprise environments — over 17,000 indexed MCP servers exist as of Q3 2026, and the National Vulnerability Database logged more than 320 CVEs referencing the protocol in 2026 alone. When an autonomous attacker and your internal AI tooling share a protocol, the question is whether your security controls understand that protocol at all.
Most do not. Traditional SIEMs were not built to parse MCP tool-call telemetry. Most EDR agents do not instrument the subprocess chains that agentic frameworks spawn. Firewall rules do not distinguish between a legitimate MCP server call from your internal AI workflow and one originating from an external agent probing your environment.
The EU AI Act Article 50 transparency obligations, which took effect for high-risk systems in August 2026, require that AI system outputs be distinguishable from human-generated actions. That requirement was written for disclosure to end users — but the operational implication for security teams is identical: if you cannot tell the difference between human-initiated and agent-initiated activity in your logs, you cannot enforce policy at that boundary.
What organizations are actually exposed to right now
The gap is not theoretical. In a tabletop exercise we ran with a mid-market financial services client in September 2026, we asked a simple question: could your SOC team distinguish an ARTEX-style autonomous attack chain from a human pentester operating on a slow, deliberate schedule? The answer was no. Their SIEM had no MCP-aware parsing rules. Their alert thresholds were calibrated to burst-scan patterns, not to low-and-slow agentic reconnaissance. Their incident response runbooks had no playbook for an attacker that could adapt its tactics between the time an analyst acknowledged an alert and the time they finished writing the ticket.
That is not a technology failure. It is a threat model failure. The tools they had were appropriate for the threat they had designed for. They had not updated the threat model.
The compliance dimension
Texas's TRAIGA and New York's pending AI Accountability Act both include provisions requiring covered entities to conduct adversarial testing of AI systems on a defined schedule. The emerging interpretation from early enforcement guidance is that adversarial testing must reflect current attack capabilities — not capabilities from the year the policy was written. An organization that conducts annual pentests using a 2023-vintage methodology and documents that as compliance with adversarial testing requirements is exposed the moment a regulator asks whether the methodology accounts for autonomous agent-based attacks.
How Intelligent iT addresses this operationally
We built our security stack to operate at the protocol layer, not just the perimeter layer. Here is how our shipped products address the specific gaps ARTEX-class threats expose.
AiT SOC Sentinel ingests MCP tool-call telemetry alongside traditional SIEM data sources. It correlates agent-initiated actions — including subprocess chains, lateral API calls, and model-context window artifacts — against behavioral baselines. When an autonomous attack chain produces the low-variance, high-cadence API call patterns characteristic of agentic execution, Sentinel flags it as a distinct threat class, not as noise.
AiT AI Gateway sits at the egress point for every AI agent your organization runs. It enforces tool-call allowlists, rate limits at the MCP layer, and logs every outbound agent action with enough fidelity to reconstruct the full attack chain during incident response. It also blocks prompt injection attempts that could redirect your internal agents into acting as reconnaissance tools for an external attacker — one of the most underappreciated attack vectors in the OWASP LLM Top 10.
AiT Audit maintains a continuously updated inventory of every AI system, MCP server, and agentic workflow in your environment, mapped to risk tier per NIST AI RMF. When the threat model changes — as it has with the public release of ARTEX — the audit surface updates automatically. You are not waiting for a quarterly review to discover you have an unmonitored MCP server that an adversary found three weeks ago.
AiT Coord manages the orchestration layer for your legitimate internal agents, enforcing least-privilege tool access and requiring human-in-the-loop confirmation for any action that exceeds a defined impact threshold. If an external agent attempts to hijack one of your internal agents through prompt injection or tool-chain manipulation, Coord's confirmation gates prevent the downstream action from executing without explicit approval.
What to do this quarter
- Audit your MCP exposure immediately. Inventory every MCP server running in your environment, whether deployed intentionally or pulled in as a dependency of a SaaS tool. Owner: your VP of Engineering or IT Operations, completed by end of Q4 2026.
- Update your threat model to include autonomous agent-based attacks. Specifically, add OWASP LLM Top 10 categories Excessive Agency, Prompt Injection, and Insecure Plugin Design to your risk register. Owner: CISO or security lead.
- Review your SOC detection rules for MCP-layer visibility. If your SIEM cannot parse MCP tool-call logs, you have a blind spot that ARTEX-class attackers will find before you do. Owner: SOC manager, timeline before end of November 2026.
- Test whether your incident response playbooks account for adaptive attackers. Run a tabletop exercise where the simulated attacker changes tactics mid-exercise. If your runbooks have no branch for that, they need revision before your next compliance audit.
- Ask your current MSP one direct question: does your SOC tooling instrument MCP traffic, and can you show me a detection rule that would fire on an ARTEX-style autonomous attack chain? If they cannot answer that question with a specific technical response, you have a gap that needs to close before year-end.
Get a compliant AI Gateway assessment before year-end
Our compliant AI Gateway white paper walks through MCP-layer enforcement, tool-call allowlisting, and the detection architecture that closes the gaps ARTEX-class tools expose. Read it before your next security review.
The bottom line
The organizations that treat ARTEX as a curiosity rather than a signal are the ones whose incident response teams will be writing the 2027 case studies. The threat model update is not optional and it is not a future-quarter item. Autonomous multi-agent attack systems are in the hands of adversaries who do not wait for your annual penetration test to find the gaps your current MSP missed.
One team
For the bold. For what's next.
Most growing firms juggle four to seven IT vendors. Our clients have one team, one number, and one invoice.
Services
What we run.
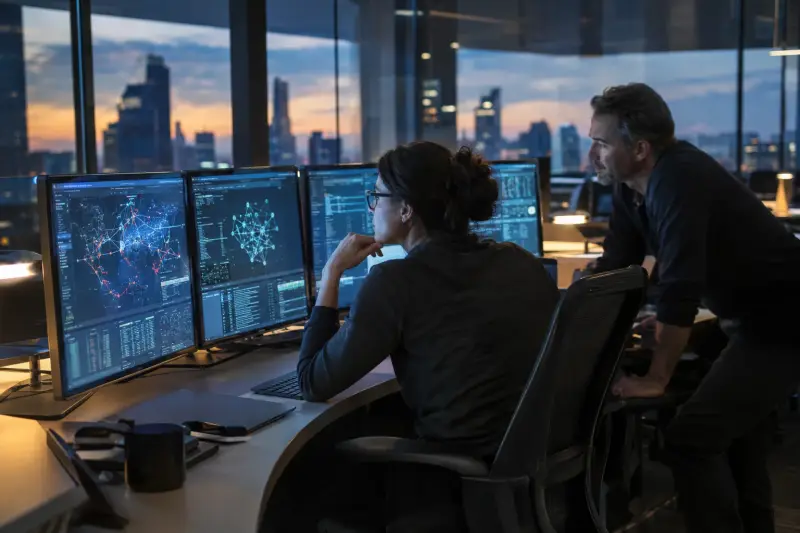
Security
24/7 security operations.
Managed SOC, Zero Trust, and audit-ready evidence for SOC 2 and HIPAA.
Managed IT
Senior engineers, no tiers.
US-based senior engineers on every ticket. Flat per-user pricing, billed annually.
AI automation
AI that does the work.
Automation handles routine IT work so your team can focus on what matters. Approved workflows cover new hires and leavers.
Build your next advantage.
Thirty minutes with a senior architect. You leave with a scope, a number, and a start date, or a straight answer that you don't need us yet.